AI Security in 2026: Protecting the Enterprise in the Age of Intelligent Automation
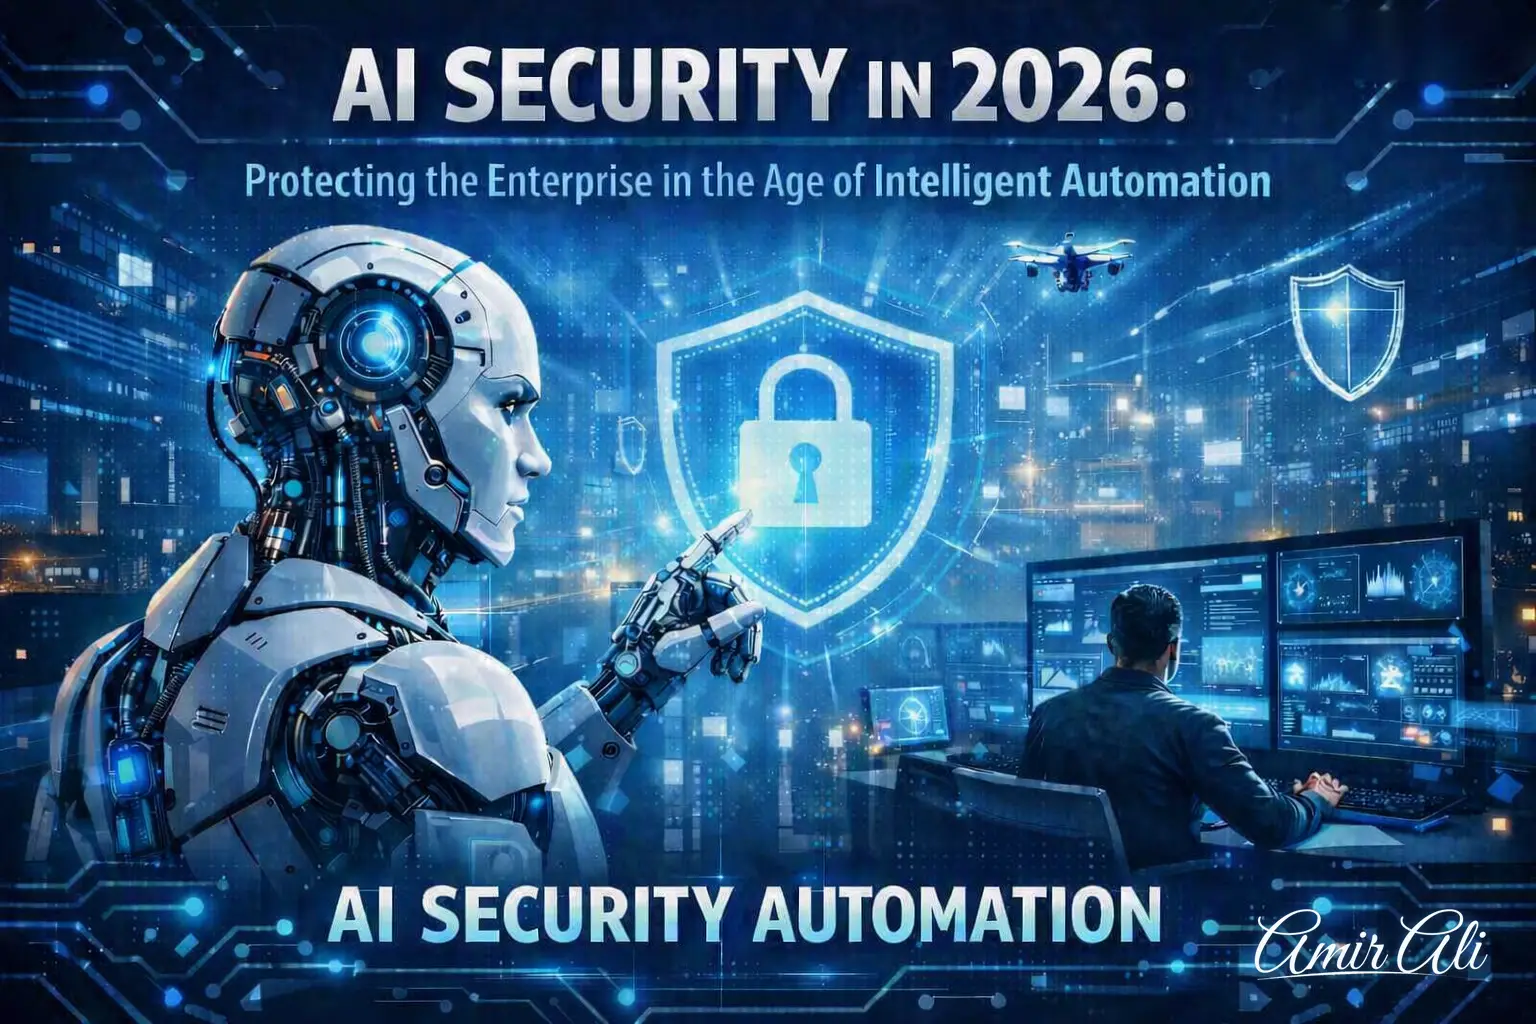
AI Security in 2026
Artificial Intelligence is rapidly becoming part of everyday enterprise operations. From Microsoft 365 Copilot and AI-powered analytics to automated workflows, intelligent assistants, and security operations platforms, organizations are increasingly allowing AI to interact with business data and make decisions at machine speed.
But as AI becomes more deeply integrated into the enterprise, a critical question emerges:
Who is securing the AI itself?
Traditional cybersecurity strategies were designed primarily around users, devices, networks, applications, and data. AI introduces another layer — intelligent systems that can understand information, generate content, interact with users, call external services, and in some cases take automated actions.
This changes the security landscape significantly.
The New Enterprise Attack Surface
AI does not replace the traditional attack surface. It expands it.
An organization implementing AI may now have to protect:
- AI models and AI services
- Prompts and instructions
- Enterprise data accessed by AI
- APIs and integrations
- AI agents and automated workflows
- User identities and permissions
- AI-generated content
- Third-party AI platforms
- Plugins, connectors, and extensions
- Training and knowledge repositories
A compromise of any of these components can potentially expose sensitive information or allow an attacker to influence automated processes.
The result is a new security principle:
Every AI interaction should be treated as a security boundary.
AI Security Is More Than Protecting the Model
When organizations discuss AI security, the conversation often focuses on protecting the AI model.
That is only one part of the problem.
The larger concern is what the AI can access and what it is allowed to do.
Consider an enterprise AI assistant connected to Microsoft 365.
If the underlying identity has access to confidential documents, emails, SharePoint sites, Teams conversations, or business applications, the AI may potentially surface information that the user already has permission to access.
This means AI security begins with something much more fundamental:
Identity security and information governance.
Strong identity controls, least-privilege access, conditional access policies, data classification, information protection, and proper permissions become even more important in an AI-enabled organization.
Prompt Injection: The New Social Engineering
One of the emerging AI security concerns is prompt injection.
Traditional phishing attempts manipulate people.
Prompt injection attempts to manipulate AI systems.
An attacker may attempt to place malicious instructions inside a document, webpage, email, or other content that an AI system processes.
For example, an AI agent may be instructed to summarize a document. Hidden or malicious instructions inside that document could attempt to influence how the AI behaves.
This creates a new security challenge because AI systems process natural language as part of their normal operation.
Security teams therefore need to consider not only:
Who is accessing the system?
but also:
What instructions and data is the AI processing?
Data Leakage Through AI
AI can create significant productivity gains, but organizations must understand exactly what information employees are entering into AI systems.
Sensitive information may include:
- Customer information
- Financial records
- Passwords and credentials
- Source code
- Business strategies
- Contracts
- HR information
- Intellectual property
- Internal security information
Organizations should establish clear policies governing what employees can and cannot submit to external AI services.
AI governance should therefore be integrated with existing Data Loss Prevention (DLP) and information-protection strategies.
AI Agents Change the Security Model
The next major shift is the rise of AI agents.
A traditional AI chatbot generally responds to a user’s request.
An AI agent can potentially:
- Understand a request
- Plan a task
- Access information
- Call APIs
- Execute workflows
- Take actions
- Report the result
This introduces a major security consideration.
An AI agent is not simply a chatbot. It can become an operational identity.
If an AI agent is given excessive permissions, a compromised prompt, account, connector, or workflow could potentially result in actions being executed with those privileges.
Organizations should therefore apply the same principles used for privileged accounts:
Least privilege.
Strong authentication.
Segmentation.
Monitoring.
Auditing.
Continuous validation.
Zero Trust Meets AI
Zero Trust architecture becomes even more relevant in an AI-driven enterprise.
The traditional principle is:
Never trust. Always verify.
For AI environments, this can evolve into:
Never assume an AI action is safe simply because the request came from an authorized user.
Every AI request should be evaluated according to:
- Identity
- Context
- Data sensitivity
- Requested action
- Application permissions
- Device security
- Risk level
- Destination
- Expected behavior
AI should receive only the access required to perform its specific function.
AI Can Also Strengthen Cybersecurity
The story is not only about risk.
AI can also become one of the strongest tools available to security teams.
Security organizations are increasingly using AI to assist with:
Threat Detection
AI can analyze enormous volumes of security events and identify patterns that may be difficult for humans to detect manually.
Security Operations
AI can help security analysts investigate alerts, correlate events, summarize incidents, and accelerate response processes.
Identity Protection
AI-driven behavioral analysis can help identify unusual login patterns, impossible travel scenarios, anomalous access, and suspicious activity.
Vulnerability Management
AI can assist security teams in prioritizing vulnerabilities based on business context rather than simply generating large lists of technical findings.
Incident Response
During a security incident, AI can help analysts quickly summarize affected systems, investigate related events, and organize response information.
The objective should not be to replace security professionals.
It should be to increase the speed and scale at which security professionals can operate.
Building an Enterprise AI Security Framework
Organizations adopting AI should consider establishing a dedicated AI security framework.
A practical framework can be built around six layers:
1. Identity
Implement strong identity governance, MFA, conditional access, privileged identity management, and least-privilege permissions.
2. Data
Classify sensitive information and control how AI systems can access, process, store, and distribute that information.
3. Applications
Evaluate AI applications, APIs, plugins, connectors, and integrations before allowing them into the enterprise environment.
4. AI Models
Assess model security, model provenance, configuration, access controls, and potential manipulation techniques.
5. Agents & Automation
Control what AI agents can execute, which systems they can access, and which actions require human approval.
6. Monitoring
Continuously monitor AI activity, access patterns, abnormal behavior, data movement, and security events.
This creates an architecture where AI is not treated as an isolated technology.
It becomes part of the organization’s overall security architecture.
Human Oversight Still Matters
One of the biggest mistakes organizations can make is assuming that AI-generated output is automatically correct or safe.
AI systems can produce inaccurate information, misunderstand context, or follow malicious instructions embedded within data.
For high-impact operations, organizations should implement appropriate Human-in-the-Loop (HITL) controls.
Examples include requiring human approval before:
- Sending sensitive communications
- Changing critical configurations
- Approving financial transactions
- Modifying privileged accounts
- Deleting enterprise data
- Executing high-risk automation
Automation should increase operational efficiency without eliminating accountability.
The Future of AI Security
The future enterprise will not simply have an AI strategy and a cybersecurity strategy.
These two disciplines will increasingly converge.
AI will become part of:
Identity → Data → Applications → Infrastructure → Security → Automation
Security teams will need to understand AI.
IT leaders will need to understand AI governance.
Architects will need to design AI-aware infrastructure.
And organizations will need to establish clear boundaries around what AI is allowed to see, understand, and execute.
The most important question will not be:
“Can we deploy AI?”
It will be:
“Can we deploy AI securely, responsibly, and at enterprise scale?”
Final Thoughts
AI represents one of the biggest technology transformations of the modern enterprise.
But every transformation creates a new attack surface.
The organizations that succeed with AI will not necessarily be the ones that automate the most.
They will be the ones that build security, governance, identity, data protection, and human oversight into their AI architecture from the beginning.
AI should not be treated as an additional application sitting on top of the existing IT environment.
It should be treated as a new architectural layer — one that requires its own security controls while remaining deeply integrated with the organization’s existing cybersecurity framework.
The future of enterprise security will not be AI versus humans.
It will be humans using secure AI to defend the enterprise at machine speed.
Key Takeaway
AI expands the enterprise attack surface — but properly governed AI can also become one of the most powerful security capabilities an organization has.
The winning architecture is not simply AI-first.
It is:
AI + Zero Trust + Identity + Data Protection + Governance + Human Oversight.